AI Agents Turn Exposed Cloud Secrets Into a Five-Minute Security Threat
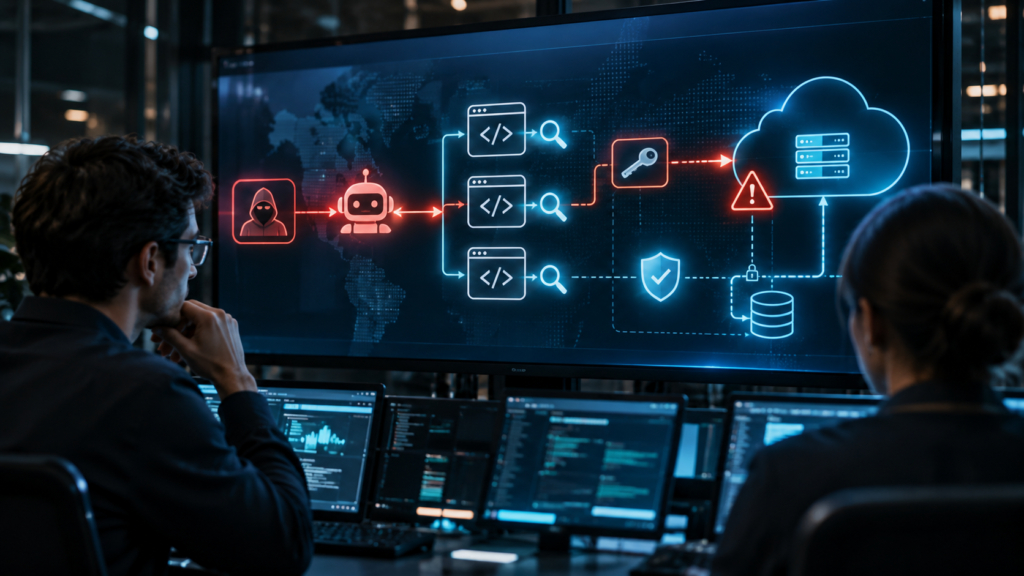
AI agents are no longer confined to defensive cybersecurity experiments. Microsoft has documented attackers using agentic AI tools to discover exposed credentials and move into cloud environments, including one case where an agent progressed from finding secrets on GitHub to extracting data from Azure Key Vault in five minutes.
FROM CODE REPOSITORIES TO CLOUD ACCESS
In research published November 5, Microsoft Threat Intelligence described attackers using agentic AI tooling, including a framework known as ARTEX, which Microsoft calls an agentic AI penetration testing framework.
Since August, attackers have used such agentic frameworks to search public GitHub repositories for exposed credentials, application secrets and AI service API keys.
Microsoft observed follow-on activity involving compromised application identities across Azure and Microsoft 365 environments.
In some cases, attackers accessed cloud storage, application settings and documents using stolen credentials.
The researchers also documented adaptive API behavior: unsuccessful requests were followed by modified API versions or methods that produced successful responses.
These observations demonstrate automated execution across several attack stages, although they do not establish that every decision occurred without human involvement.
Source: Microsoft Threat Intelligence, November 5, 2026
WHY AGENT IDENTITY MATTERS
The attacks exploited existing weaknesses in application credentials and cloud permissions.
An agent possessing a valid credential can exercise whatever access that identity permits, regardless of whether the activity is legitimate.
Cisco's March announcement addressed this broader problem through agent identity management, Zero Trust controls and policy enforcement for Model Context Protocol connections.
These defensive capabilities were not tested against the Microsoft cases in the cited materials.
Source: Cisco, March 23, 2026
EMERGE TIMES ANALYSIS: AUTONOMY COMPRESSES RESPONSE TIME
The significant development is not that AI invented credential theft. Exposed secrets and excessive application permissions have been security problems for years.
What changes is the speed at which automated systems can connect discovery, authentication, cloud reconnaissance and data access.
Traditional security workflows often assume meaningful time between an initial exposure and consequential misuse.
Agentic automation can shrink that interval dramatically.
For enterprises deploying legitimate AI agents, the lesson extends beyond cybersecurity teams.
Every autonomous worker using APIs, cloud services or MCP tools inherits the risks associated with its credentials and permissions.
The relevant benchmark is therefore not simply how many tasks an agent can complete independently.
It is whether its authority remains limited, observable and rapidly revocable when something goes wrong.
In the Agentic Age, execution speed is becoming both a productivity advantage and a security liability.
Sources
- Microsoft Threat Intelligence — Threat Actors Use Agentic AI Tooling to Find and Abuse Exposed Secrets, November 5, 2026
- Cisco — Cisco Reimagines Security for the Agentic Workforce, March 23, 2026
Editorial Note: The attack observations originate from Microsoft's security investigation. Cisco's announcement provides architectural context, not confirmation of the specific cases.
This article was prepared with AI assistance and reviewed by an Emerge Times editor before publication. Licensed CC BY 4.0: credit “Emerge Times (emergetimes.com)”. Usage & License. Featured images are AI-generated illustrations; any logos shown are trademarks of their owners, and Emerge Times is not affiliated with them.