Canonical opens opt-in Edge archive with AI-written Ubuntu security fixes
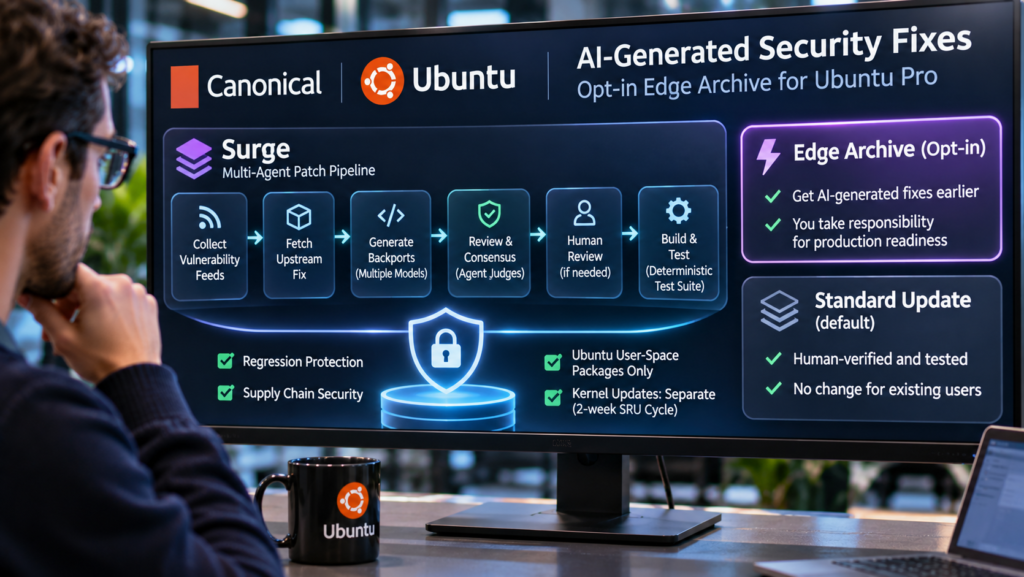
Canonical now lets Ubuntu Pro subscribers deploy AI-authored security fixes ahead of the point at which its own engineers complete their review and testing, Help Net Security reported on 18 November 2026. The fixes are produced by Surge, a system Canonical developed for known flaws in Ubuntu’s userspace software, meaning everything outside the kernel. Delivery runs through the Edge archive, a new channel that customers must choose to turn on.
What changes for customers
Subscribers who leave Edge disabled see no difference: the regular security updates are still validated by people before they are released. Enabling Edge brings fixes sooner, but the customer takes over a responsibility that Ubuntu’s testing usually carries, which is judging whether a patch is safe enough for production.
Canonical frames this as a matter of speed. Its security teams have released twice as many fixes as in the previous year, and the company says AI agents are fueling a flood of vulnerability reports and attacks throughout open-source projects. Manual review and soak testing, where a fix runs for a prolonged period so problems surface before release, take longer than some customers are prepared to stay exposed. The company summed up its position this way:
“we need to fight AI with AI.”
How Surge works
Surge hands work along a chain of AI agents, each responsible for one step. The first ingests vulnerability feeds, links each report to Ubuntu packages and discards the ones irrelevant to Ubuntu. The second fetches the upstream fix together with the code around it. Multiple competing models then independently produce a backport, which adapts a fix written for a program’s latest version so that it fits the older version carried by a long-lived Ubuntu release.
Next, a group of distinct judge models examines the candidates and has to agree on an outcome. When the judges are split, unsure, or facing something atypical, the patch is routed to a member of Ubuntu’s security team. Patches that clear this stage are compiled and subjected to the identical deterministic test suite applied to every other package in the distribution. Canonical says the arrangement protects against regressions and against supply-chain attacks, in which malicious code enters software through its build or update path.
What Surge leaves out
Kernel fixes are excluded. Canonical says kernels need a separate backporting method, and simply shipping the newest kernel version would carry a large stability risk for enterprise systems. Kernels therefore follow a two-week Stable Release Update cycle, with cycles overlapping so that a new proposed kernel appears each week.
Surge is also meant for the backlog of already-known vulnerabilities. Newly found flaws, including those surfaced by Canonical’s automated research, continue through coordinated disclosure: private reporting, then work with upstream maintainers under embargo before anything is made public. Canonical said it strongly disagrees with those who have dropped that practice.
Why it matters for agents
Surge is a concrete example of a multi-agent pipeline with a defined handoff to humans. Its routing rule, under which disagreement, low confidence or unusual cases go to a person, is a pattern that other automated operations might borrow. The source does not say how often escalation happens.
The Edge archive also shifts a decision to the customer. Teams that use automated update tooling or agents to manage Ubuntu fleets would need a policy on whether those systems may pull from Edge, and on what testing should replace the soak period. The source does not state how long patches remain in Edge before regular release, or how regression rates are measured, so those points are unclear. Canonical’s statements about protection against regressions and supply-chain attacks are its own, and the report does not assess them independently.
Sources
- Ubuntu AI security patches are here, if you’re willing to test them yourself — helpnetsecurity.com
This article was prepared with AI assistance and reviewed by an Emerge Times editor before publication. Licensed CC BY 4.0: credit “Emerge Times (emergetimes.com)”. Usage & License. Featured images are AI-generated illustrations; any logos shown are trademarks of their owners, and Emerge Times is not affiliated with them.